Energy and security belong together
On this page
- Energy is more than electricity and gas
- When digital systems disrupt physical installations
- Energy supply as a strategic target
- Where energy management and cybersecurity meet
- A technical fault or a cyberattack: how do you tell the difference?
- How cyber-secure is a company's energy supply?
- From insight to resilience
- European legislation is bringing both worlds closer together too
- Energy remains the starting point
- Sources and further reading
Energy is one of the most fundamental needs of every European economy. Hospitals, industry, food chains, data centres, public transport and households all depend on a reliable energy supply. Without electricity, gas, heat or cooling, it is not only business operations that come under pressure. The safety of people, the continuity of essential services and ultimately the stability of our society can be affected as well.
That dependence is also greater than we realise day to day. According to Eurostat, the European Union relied on net imports for 57.3 percent of its energy needs in 2024. International trade flows, geopolitical developments and the availability of energy infrastructure therefore have a direct bearing on our energy security.
But energy security has another dimension. The installations we use to produce, transport, convert and use energy are increasingly controlled digitally. That brings opportunities for efficiency and flexibility, but also new vulnerabilities.
Recent cyberattacks on refrigeration systems in French supermarkets and the continuing Russian attacks on Ukraine's energy infrastructure show, in very different ways, how closely energy and security are linked.
That raises a question that is becoming more relevant for Dutch businesses too: how secure is our energy supply, really?
Energy is more than electricity and gas
When we talk about energy security, we quickly think of power grids, gas pipelines and power stations. But for many businesses the actual dependence is considerably broader.
An industrial manufacturer, for example, needs not only electricity to drive machines, but also heat, steam or compressed air to keep production processes running. A data centre depends on electricity and cooling. In hospitals, emergency power, medical equipment, climate control and the refrigerated storage of medicines are essential. For food producers, distribution centres and supermarkets, temperature control is directly tied to product quality and food safety.
Strictly speaking, cold is not a form of energy in its own right: cooling works by using a refrigeration process to remove heat from a space or product. From an operational point of view, however, keeping enough cooling capacity available is just as important as the supply of electricity or heat.
That distinction matters. An organisation can have a fully functioning electricity connection while its production process still comes to a halt because the refrigeration system no longer works properly.
Energy security is therefore not only about the availability of kilowatt hours. It is ultimately about the availability of the energy-related processes and facilities an organisation needs to operate safely and reliably.
The International Energy Agency (IEA) defines energy security as the uninterrupted availability of energy sources at an affordable price. For individual businesses, that definition deserves a practical addition: energy must not only be available, it must also be converted, distributed and used safely.
When digital systems disrupt physical installations
How tangible that digital dependence is became clear in France on 12 October 2026.
Attackers managed to manipulate, remotely, the systems that controlled the refrigeration of hundreds of supermarkets. Temperature and defrost settings were changed, in some cases to values of 50 degrees Celsius. The consequences were considerable: stores had to destroy fresh and frozen products, and fires at refrigeration equipment were even reported.
The attack hit stores of Intermarché, Carrefour, Monoprix and Coopérative U, among others. The parties involved estimated the financial damage at many millions of euros.
The French government agency CERT-FR confirmed on 12 October that remotely accessible refrigeration controllers had been compromised. In the following days it was confirmed that systems from Danfoss, Copeland and Dixell, among others, were involved.
It is precisely the nature of this attack that makes it stand out. The electricity supply of the affected stores did not need to be interrupted to cause considerable physical and economic damage. The attackers interfered with the digital control of installations that are essential to the business.
A similar problem was reported on 2 November 2026 at several Belgian Delhaize stores. According to RTL Belgium, temperatures in refrigeration and freezer units rose unexpectedly, in some cases to around 15 degrees. Store operators had to throw products away as a result. According to RTL, it was a cyberattack in which the defrost mode of the refrigeration was switched on remotely; Delhaize itself spoke of an IT incident. A refrigeration company saw the same method as in France, but whether the same attackers were behind it was not known.
In addition, parent company Ahold Delhaize faced a separate cybersecurity incident in October. The group confirmed on 19 October that malicious activity had been detected within its IT infrastructure, after which several digital systems were taken offline as a precaution. This affected online ordering and services, among other things. There is no proven link between that incident and the attacks on French refrigeration systems.
These events show that cyber incidents are not limited to data breaches, websites or office IT. They can also reach into physical processes: from temperature control and product storage to industrial production and logistics.
And that makes protecting such systems an energy issue as well.
Energy supply as a strategic target
The link between energy and security is visible on a larger scale in the war in Ukraine.
Since autumn 2022, Russia has repeatedly attacked Ukrainian power stations, substations, transmission grids and heating infrastructure. Missiles and drones, among other weapons, are used to physically damage the energy supply or put it out of action.
According to a report by the UN human rights monitoring mission of 29 June 2026, at least 423 attacks on infrastructure for electricity generation, transmission and distribution were recorded between October 2025 and March 2026, in addition to at least 74 attacks on heating plants and other heating facilities.
The attacks continued in October 2026 as well. After Russian missile and drone attacks on 19 October, at least 550,000 households were left without electricity, according to reporting by Dutch broadcaster NOS.
The consequences reach far beyond the electricity supply itself. Without power, water pumps, heating systems and communication systems can fail. Hospitals have to fall back on emergency facilities, logistics are disrupted and homes can become uninhabitable during harsh winters.
The UN describes these interdependencies as a major cause of the extensive humanitarian harm. On 26 October 2026, the independent international commission of inquiry of the United Nations concluded that, through their sustained attacks on Ukraine's energy infrastructure, Russian authorities have committed war crimes and crimes against humanity.
The war thus shows that energy infrastructure does not only have economic value, but is also of strategic importance to the security and resilience of a society.
Although the physical attacks in Ukraine differ fundamentally from the cyberattacks on French supermarkets, both touch on the same principle: when energy-related systems are disrupted, the consequences can quickly spread to other social or economic functions.
Where energy management and cybersecurity meet
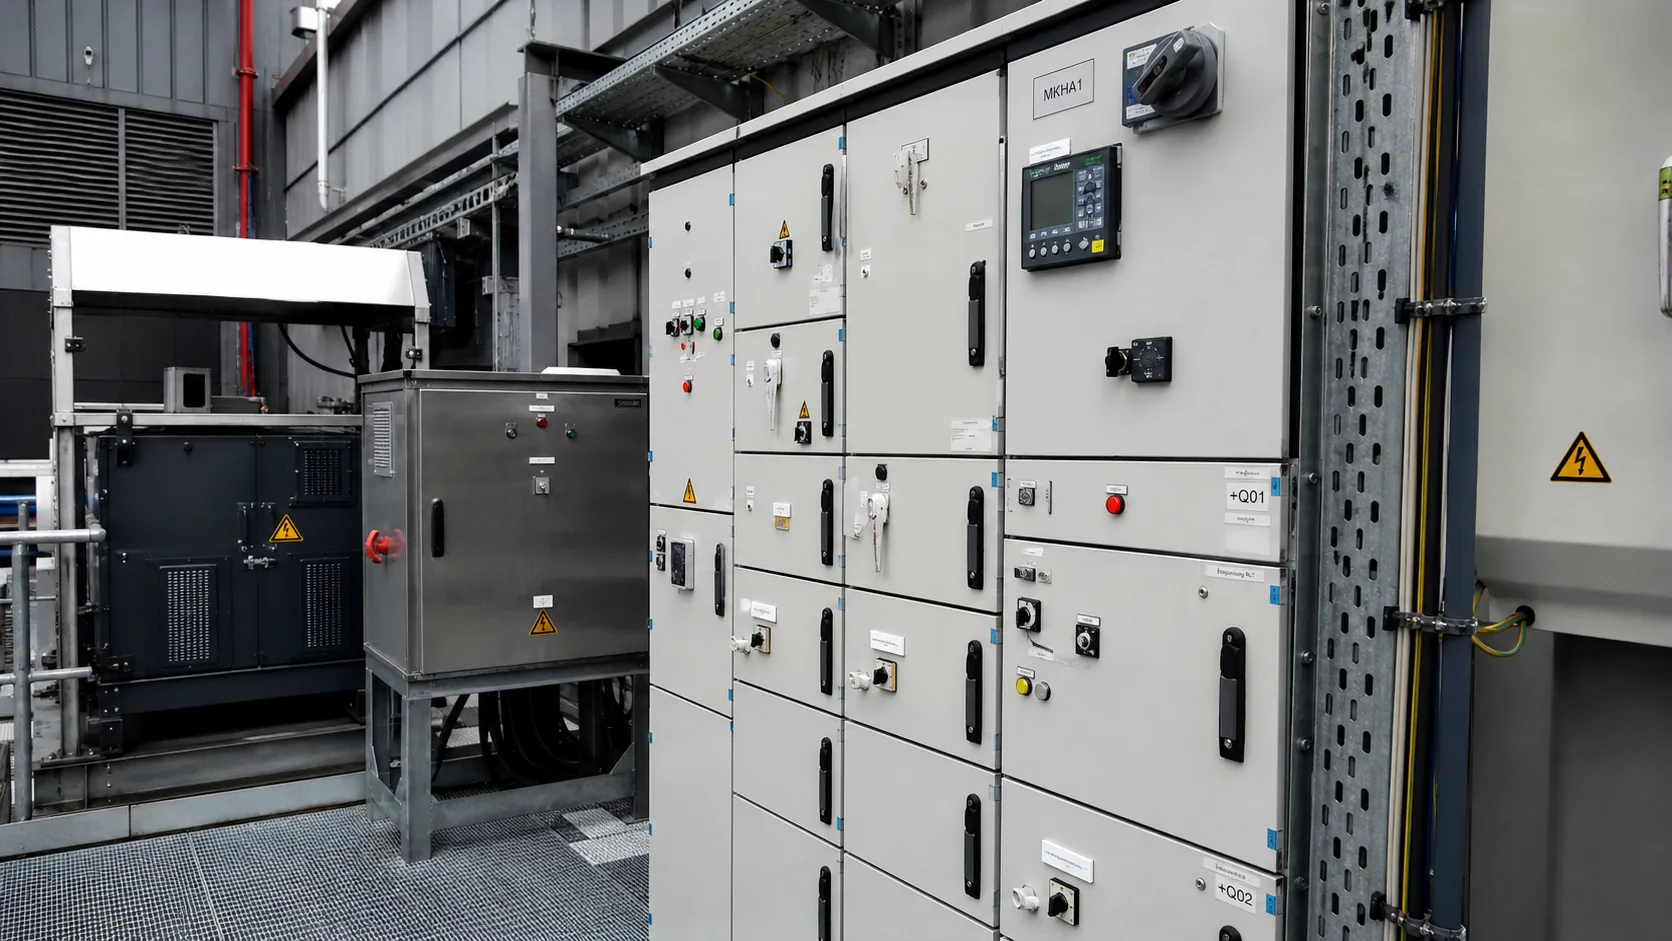
The energy transition increases the importance of digitalisation. Solar panels, battery storage systems, heat pumps, charging points, building management systems and industrial installations are more and more often monitored and controlled remotely.
Energy management is becoming smarter as a result. Businesses can match production and consumption more precisely, limit peak loads, store energy or respond flexibly to market conditions.
To make this possible, various digital systems are connected to one another. Think of energy management systems (EMS), building management systems, industrial process controllers, sensors and monitoring platforms.
The technology behind these installations is often referred to as Operational Technology (OT): hardware and software that monitor and control physical processes. This includes industrial control systems such as PLCs and SCADA systems.
Where traditional IT focuses mainly on processing and protecting information, OT has a direct effect on the physical world. A digital command can start a pump, open a valve, switch off a compressor or change the charging strategy of a battery.
The Dutch National Cyber Security Centre (NCSC) stresses that OT systems are now frequently connected to business networks and the internet. At the same time, these systems often have a long technical lifespan, and software updates or security measures cannot always simply be applied, because the continuity and safety of physical processes come first.
This is where energy management and cybersecurity overlap.
The more influence digital systems gain over our energy supply and energy-related processes, the more their reliability and security matter.
That does not mean digitalisation automatically leads to a less secure energy supply. Digital monitoring can in fact make faults visible sooner and help installations run more efficiently and reliably.
But those benefits call for a conscious approach to access rights, software, external connections and dependence on suppliers.
A technical fault or a cyberattack: how do you tell the difference?
It is exactly at this intersection that an interesting scientific question arises.
Suppose the electricity consumption of a refrigeration system suddenly rises sharply while the temperature climbs at the same time. That can be caused by a faulty sensor, a mechanical failure, a wrong setting or a cyberattack.
For the operator, the first visible symptoms may be almost identical. The installation behaves abnormally, but the cause is not immediately clear.
In September 2026, the scientific International Journal of Information Security published a systematic literature review of methods for distinguishing cyberattacks from technical faults in smart power grids.
The researchers found that only six of the 25 studies reviewed explicitly tried to distinguish malicious digital manipulation from ordinary technical anomalies. Moreover, much of the available research was based on simulations rather than field tests.
That illustrates how complex it is to assess cybersecurity and process safety together.
The answer does not lie only in adding more cybersecurity software. Combining different sources of information matters too.
An energy management system can, for example, detect an unusual change in electricity consumption. An independent temperature monitoring system can at the same time establish that a refrigeration process is moving outside its safe limits. Logs from the process control system can then help determine whether unexpected settings have been changed.
When technical, energy and digital data are analysed together, a more complete picture of the state of an installation emerges.
It is essential that critical safety measurements and safeguards do not depend entirely on the same control system that may have been compromised.
How cyber-secure is a company's energy supply?
For energy-intensive businesses, answering this question starts with insight into their own dependencies.
A traditional energy analysis, for example, maps electricity and gas consumption, connection capacity and the energy volumes required. A continuity analysis examines what happens when an energy carrier is temporarily unavailable.
But a complete assessment needs an extra dimension: the digital systems that determine how energy is used.
It helps to answer three questions together.
1. Is the energy we need available?
Which processes depend on electricity, gas, heat, steam, compressed air or cooling? How long can they keep running without these before damage, downtime or safety risks occur?
2. Do the installations remain controllable?
Which systems govern the conversion and distribution of energy within the company? Can installations operate on their own if their cloud connection, business network or external management platform fails?
3. Is the control reliable?
Who can change settings? Which suppliers have remote access? How do you establish that measurements and commands can be trusted? And what happens when a system does not fail, but carries out the wrong commands?
Together, these questions form a practical basis for mapping the digital and physical vulnerability of energy processes.
An important next step is to develop scenarios that combine different disruptions.
What happens, for example, when a refrigeration system is controlled incorrectly while there is enough electricity available? Can a battery still operate safely when the energy management system cannot be reached? Or can essential processes continue when both the grid connection and a digital control link are disrupted?
Scenarios like these help to understand not only the likelihood of failures, but above all their consequences for safety and business continuity.
The approach fits international methods for risk management. The NIST framework for OT security and the industrial security standard IEC 62443 describe how organisations can systematically assess technical systems, access rights and operational risks.
Existing process safety methods, such as HAZOP and Bow-Tie analyses, can also be combined with cybersecurity risk analyses. The NCSC explicitly recommends this integrated approach.
From insight to resilience
A completely risk-free energy supply does not exist. Power grids can be disrupted, installations can break down and digital systems can be attacked.
That is why, besides preventing incidents, the ability to cope with disruptions matters most.
The international literature often uses the term resilience for this: the ability of a system to absorb disruptions, maintain essential functions and then recover in a controlled way.
For businesses, this means physical and digital measures have to reinforce each other.
Emergency power can protect against a power cut, for example, but offers no solution when the control of an installation has been compromised. Conversely, a well-secured control system cannot prevent a physical interruption of the power supply.
A resilient organisation therefore pays attention to both situations.
Think of separate networks for office IT and industrial installations, controlled access for maintenance partners, up-to-date and tested recovery procedures, independent alarms and the ability to stop critical processes safely when problems arise, or to operate them manually where that is responsible.
Emergency power, redundancy, thermal buffers and alternative energy supplies also deserve attention, depending on the risks and technical possibilities of the business.
An important principle is that backup facilities must be genuinely independent and usable. An emergency generator that depends on a compromised control system, for example, offers less protection than it appears to on paper.
After the attacks on refrigeration systems, the French cybersecurity authorities advised, among other things, not to expose management interfaces directly to the internet, to use secure connections and to check firmware and configurations.
The broader lesson is that a continuity plan should account not only for the loss of energy, but also for the loss of control over the installations that use energy.
European legislation is bringing both worlds closer together too
The European Union increasingly recognises that physical and digital security have to be assessed together.
On 15 August 2026, the Cyberbeveiligingswet (Cybersecurity Act) and the Wet weerbaarheid kritieke entiteiten (Critical Entities Resilience Act) came into force in the Netherlands. They transpose the European NIS2 Directive and CER Directive, respectively, into Dutch law.
The Cybersecurity Act focuses on digital resilience, risk management and the handling of cybersecurity incidents. The Critical Entities Resilience Act addresses more broadly the physical and organisational resilience of designated organisations that provide essential services.
Not every energy-intensive business automatically falls under both acts. Whether they apply depends on factors such as the sector, the activities, the size and any designation as a critical entity.
The underlying principles are relevant for businesses outside their direct scope as well.
The European Commission has also developed specific cybersecurity rules for cross-border electricity flows. The European network code on cybersecurity recognises, among other things, that combining existing energy systems with new digital technology creates particular risks, including cascading effects during disruptions.
In August 2026, the European association of transmission system operators, ENTSO-E, published recommendations for securing critical electricity infrastructure. It stresses that security of supply, physical security and cybersecurity have to be approached together.
That is an important development: the reliability of our energy supply is increasingly seen as the result of several interdependent forms of security.
Energy remains the starting point
For many Dutch businesses, energy management has traditionally focused on availability, affordability, procurement, consumption and sustainability. In recent years, issues such as grid congestion, flexibility, local generation and energy storage have been added.
Cybersecurity adds a new dimension.
A battery, after all, is not only a storage facility, but usually also a digitally controlled system. A refrigeration system is not only an energy consumer, but also a process whose operation can be influenced digitally. And an energy management system is not only a way to use energy more intelligently, but can also be an important part of day-to-day operations.
For COMCAM, the starting point is energy. Not in the role of a cybersecurity specialist, but from the understanding that reliable energy is of great importance to businesses and that digital systems play an ever larger part in it.
By looking at energy dependencies, physical facilities and digital control together, organisations can better understand where their vulnerabilities lie and which measures they need to protect their continuity.
Cooperation between energy experts, technical managers and cybersecurity specialists is essential here.
Because energy security ultimately means more than the guarantee that energy is available. It also means that organisations can trust their energy supply to keep functioning safely, reliably and under control.
And that is precisely why energy and security belong together.
Sources and further reading
Energy security and European dependence
- Eurostat: Energy in Europe, imports dependency, 18 March 2026.
- International Energy Agency: Glossary, energy security.
- ENTSO-E: Position Paper on the Security of Critical Infrastructure, 31 August 2026.
- European Commission: Critical infrastructure and cybersecurity.
Cyber incidents and refrigeration systems
- CERT-FR: security alert on refrigeration systems, 12 October 2026, updated 16 October.
- Euronews: Hundreds of French supermarkets hit by cyberattack on refrigeration systems, 12 October 2026.
- Al Jazeera: Hundreds of supermarkets in France hit by unprecedented cyberattack, 13 October 2026.
- RTL Belgium: refrigeration problems at Delhaize, 2 November 2026.
- Ahold Delhaize: update on the cybersecurity incident, 19 October 2026.
Ukraine and strategic energy security
- UN human rights monitoring mission: attacks on Ukraine's energy infrastructure, 29 June 2026.
- UN commission of inquiry: conclusions on Russian attacks, 26 October 2026.
- NOS: hundreds of thousands of households without power in Ukraine (in Dutch), 19 October 2026.
Cybersecurity, OT and scientific research
- NCSC: getting started with securing OT/IACS (in Dutch).
- NIST: Guide to Operational Technology Security, SP 800-82 Rev. 3, September 2023.
- MITRE: ATT&CK for Industrial Control Systems.
- ENISA: Threat Landscape 2026, 22 September 2026.
- Sechi et al.: Towards distinguishing cybersecurity attacks and safety faults in DER-rich smart grids, International Journal of Information Security, September 2026.
- Vigneshwaran et al.: Cyber attack detection in smart grids, a survey, Computer Science Review, May 2026.
Dutch legislation
- Dutch government: Cybersecurity Act and Critical Entities Resilience Act in force (in Dutch), 15 August 2026.
Sources consulted on 2 November 2026. Ongoing incident investigations may lead to new insights.
Does this apply to your business?
Our energy specialists are happy to look at what this means for your connections, your contract and your purchasing situation. Without obligation.